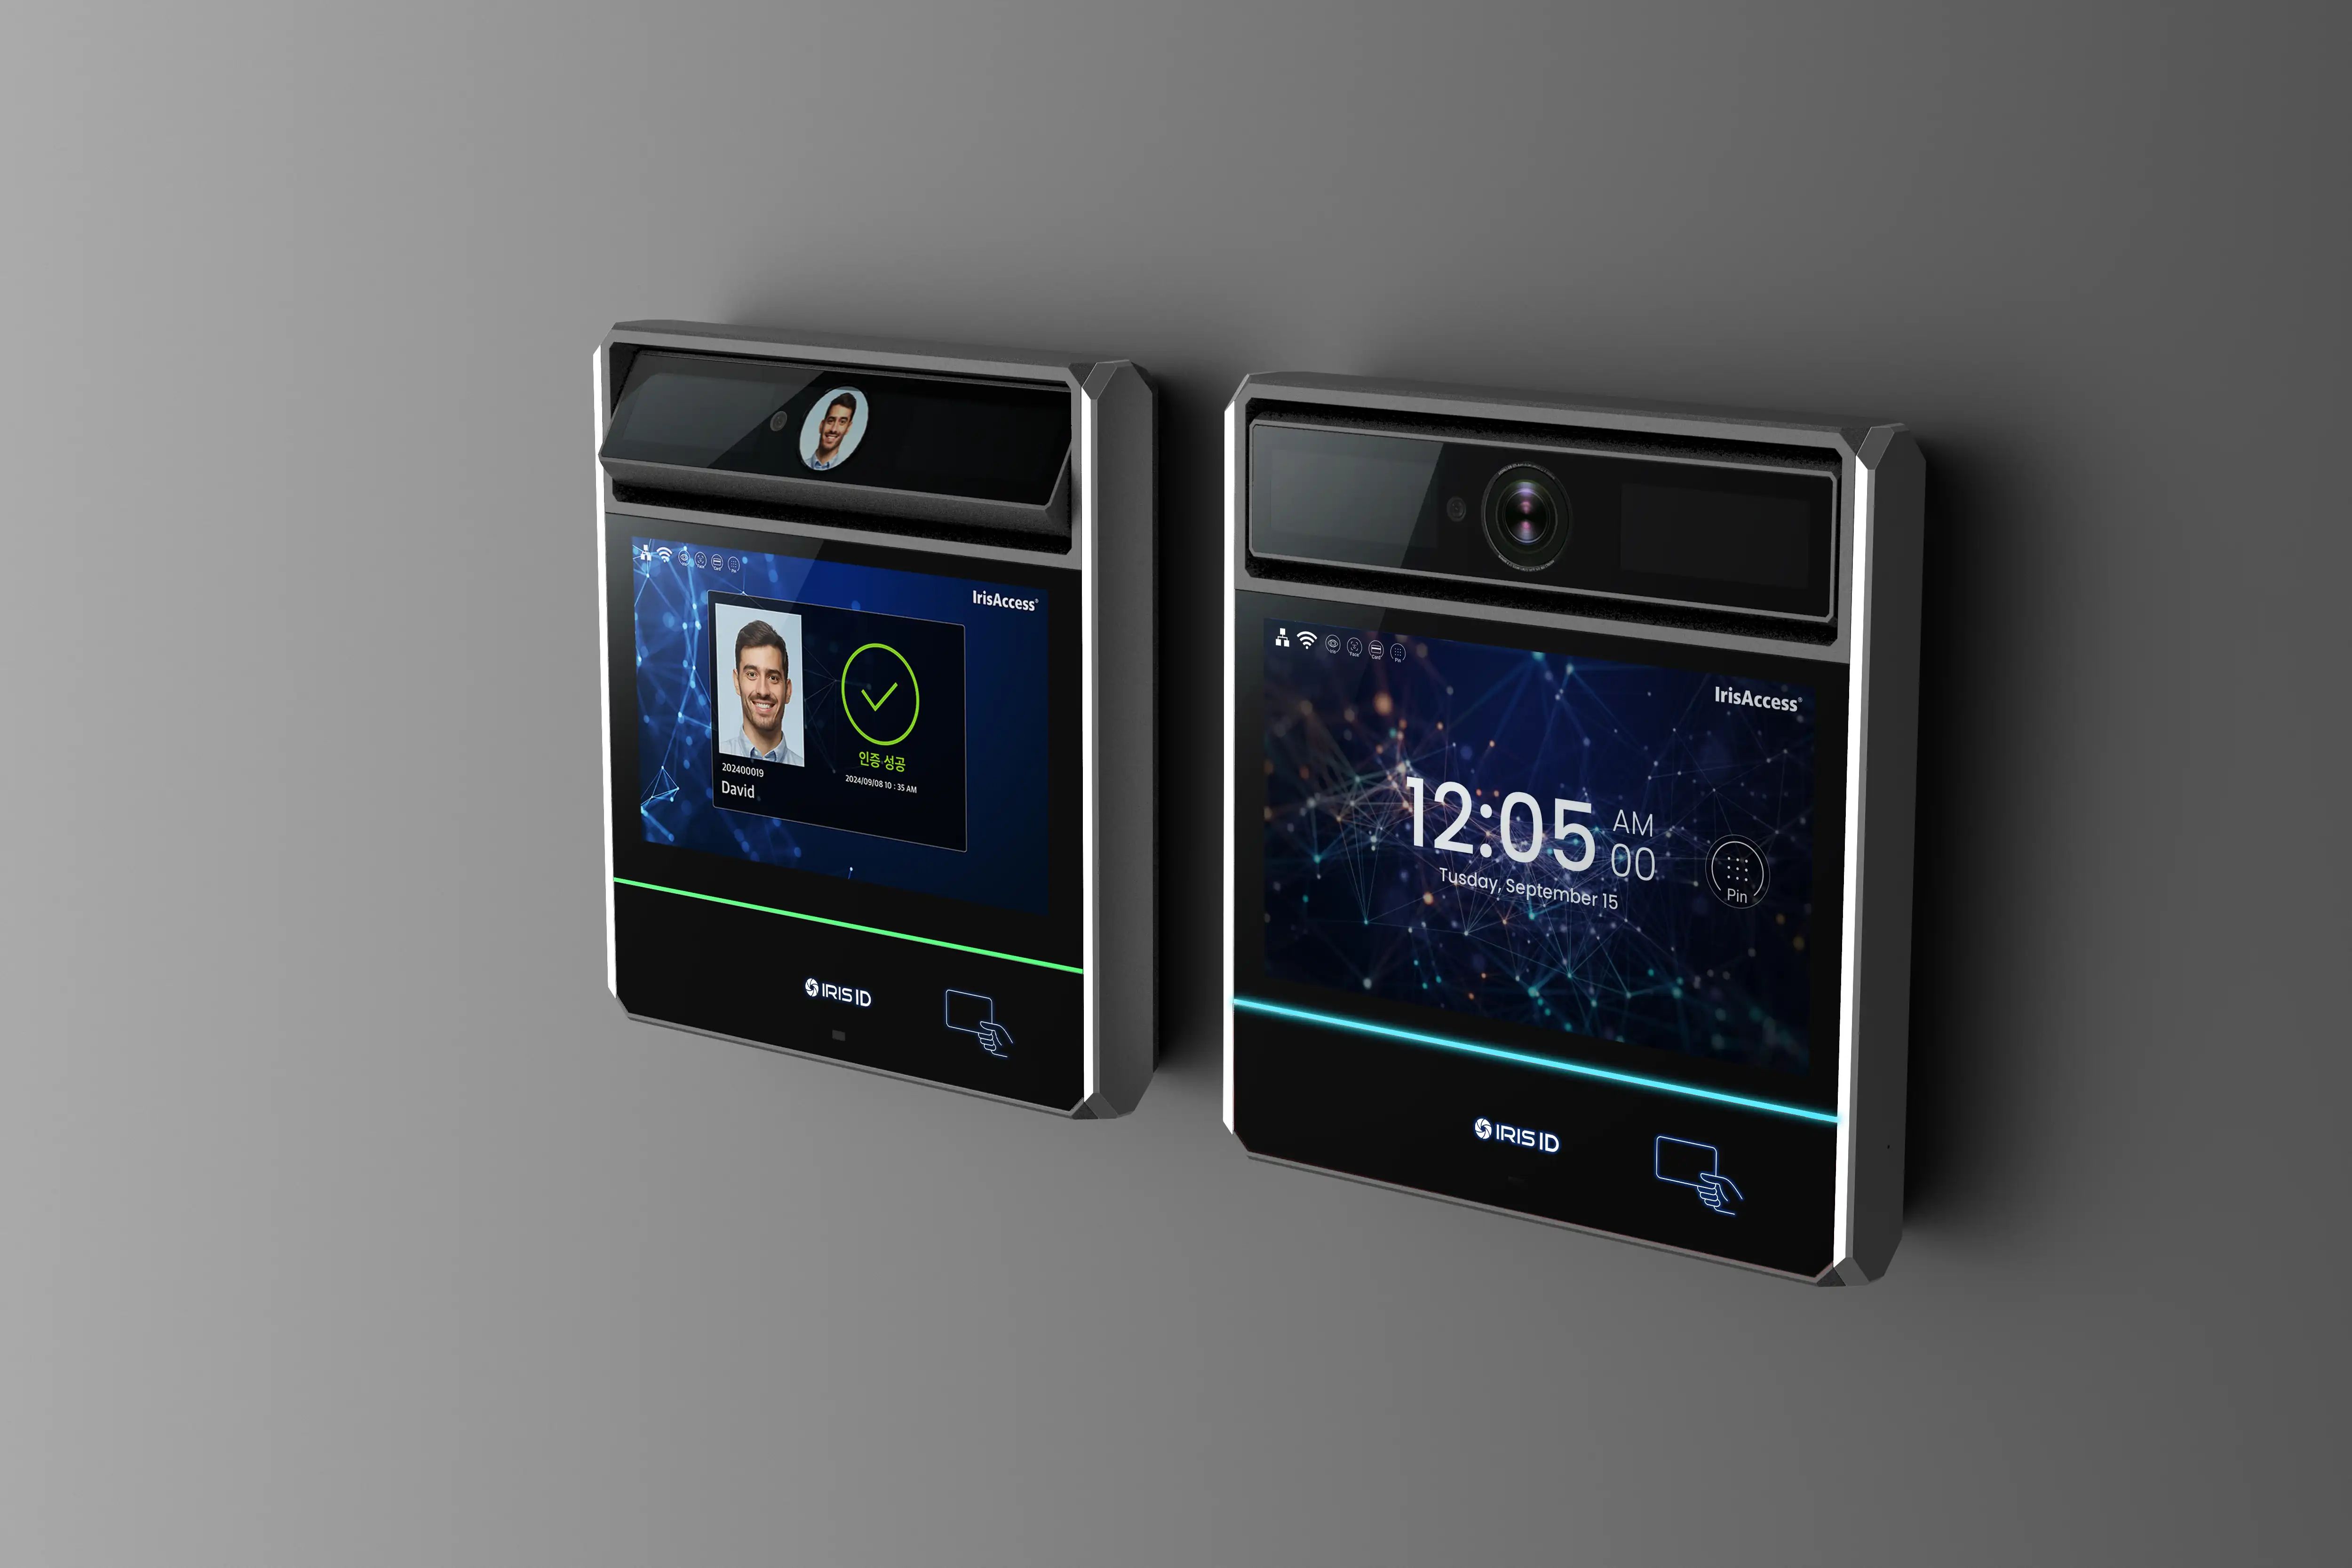
Sigur has completed development of an integration with Iris ID biometric terminals. The joint solution combines iris and face recognition with various combinations of biometric identification and access cards. Users, their access rights and events are managed in Sigur software. The integration supports IrisTime iT100 and IrisAccess iA1000 terminals and is already available for commercial use.
Unlike traditional credentials, such as access cards, biometric identification makes it possible to verify not only a person's authorization to enter but also their identity.
For contactless identification, Iris ID technology uses the unique patterns of the iris, which do not change with age. This method is particularly relevant for high-security facilities, where it is important to prevent unauthorized entry using someone else's credentials.
Integration with Sigur makes it possible to use these capabilities within a unified access control system. Iris ID terminals perform biometric recognition, while Sigur controllers verify users' access rights and make access decisions in accordance with the configured rules.
Modern access control must go beyond determining whether a credential has permission to enter. Organizations increasingly need confidence that the person requesting access is genuinely the person who has been authorized. Our integration with Sigur brings together identity authentication and access authorization in a frictionless environment, allowing customers to strengthen security without introducing unnecessary friction for users.
The partnership reflects both companies' commitment to interoperability, open integration and customer choice, allowing system integrators and end users to deploy advanced biometric authentication as part of a broader physical security strategy.
By connecting who the person is with where that person is authorized to go, Iris ID and Sigur are creating a more secure, intelligent and frictionless approach to physical access control.
One of the key advantages of the integration is the ability to manage biometric data and users directly in Sigur software.
Iris templates are enrolled using an Iris ID terminal connected to the system. The resulting templates are encrypted, stored and automatically distributed to devices installed at access points where the user is authorized to enter.
Photos, identifiers and other user data are synchronized in the same way. When access rights change, Sigur automatically updates the information on the relevant terminals. This eliminates the need for administrators to manually add employees and update their details on each device.
For facial recognition, existing employee photos can be used to generate biometric templates. This simplifies system setup at facilities with large numbers of users.
The integration supports several identification methods: iris recognition, facial recognition, access cards, and combinations of these methods.
For example, biometrics can be used as the sole identification method at certain access points, eliminating the need for physical cards. In areas with higher security requirements, two-factor authentication can be configured: employees first present an access card and then verify their identity using iris recognition.
Contactless iris recognition is also convenient in environments where employees wear personal protective equipment (PPE), including gloves and face masks. If an iris template has been enrolled, recognition is possible even using just one eye.
The joint solution also supports Wiegand 26, 34 and 58.
Standalone operation and secure communicationBiometric templates and identifiers are stored directly in the memory of Iris ID terminals. This means that recognition is performed locally, without using the processing resources of the Sigur server.
Even if the connection to the server is lost, the terminal can continue identifying users. The data is transmitted to a Sigur controller, which makes access decisions based on the rules and restrictions stored in its local memory.
Communication with controllers uses the OSDP protocol or Wiegand, which supports encryption. Network communication between the terminals and the integration service is carried out over HTTPS.
Access granted and access denied events, recorded access events and terminal connection status are available in Sigur for monitoring and further analysis.
A solution for existing and new facilitiesThe integration can be used at industrial facilities, data centers, critical infrastructure sites and other organizations where reliable identity verification is required.
The solution is not limited to employees: temporary visitors can also be assigned access rights and identified using biometrics.
The new integration of Sigur with Iris ID biometric terminals marks an important step in the development of our ecosystem. We have remained true to the key principles of Sigur integration: full management of biometric templates remains within the system, communication with devices is monitored in real time, and support for combining different types of identification allows for the creation of complex access logic. By utilising the iris, our users gain access to a highly accurate identifier that remains virtually unchanged over time, whilst all data transmission is secured via the HTTPS protocol.
The integration is supported in Sigur software version 1.8.5.69 and later. The integration service is available for Windows and Linux. Licensing is based on the number of connected biometric terminals.
To learn more about how Iris ID integration can enhance your Sigur access control system, contact our sales department.


